Shop-Script Plugin Updates: A Safe Testing and Release Checklist
A plugin update should leave more than the installation screen in a healthy state. Here is a release workflow for Shop-Script businesses that depend on catalogue, checkout, stock and third-party integrations. Why updates need more than a green button A Shop-Script store may depend on plugins...
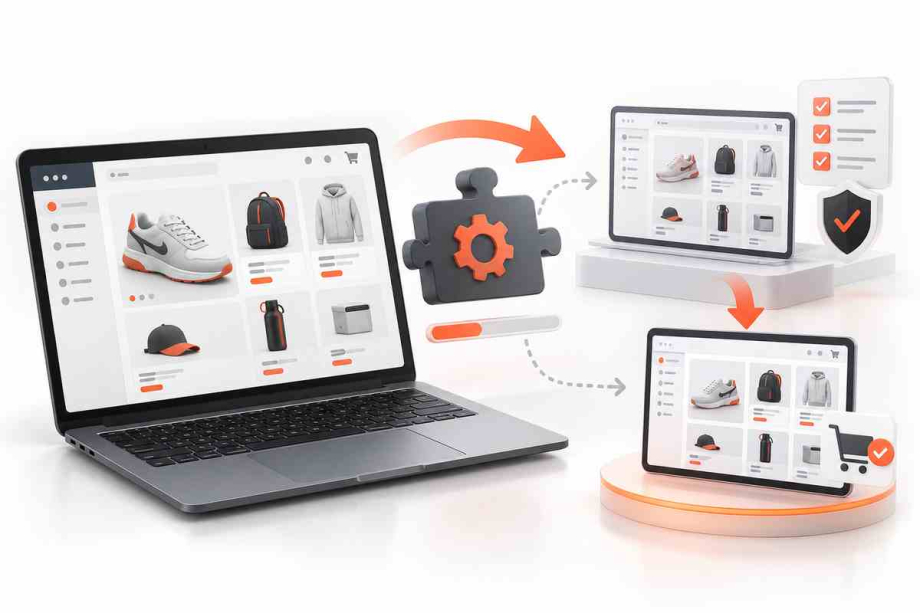
A plugin update should leave more than the installation screen in a healthy state. Here is a release workflow for Shop-Script businesses that depend on catalogue, checkout, stock and third-party integrations.
Why updates need more than a green button
A Shop-Script store may depend on plugins for payment callbacks, shipping quotations, product filters, stock changes and marketplace feeds. Updating one component can affect another even when the shop homepage looks normal. This is particularly important when code has been customised or a theme calls plugin methods directly. A responsible release is therefore a small operational project: identify the change, reproduce current behaviour, test representative journeys, deploy with a recovery path and observe the result. The aim is not to avoid updates indefinitely; it is to make each update understandable, reversible where possible and proportionate to its business risk.
Treat a security fix, a new sales feature and a cosmetic admin adjustment differently. Urgency matters, but urgency should change the scope of testing rather than eliminate it. Identify the person who can approve business behaviour, not only the developer who installs the package. If the team cannot describe what “working” means for an order, stock change or refund, a successful installation message is not enough evidence.
Map dependencies before touching production
Create a compact inventory of Webasyst framework version, Shop-Script version, active theme, custom plugins, payment and shipping integrations, scheduled jobs and external APIs. Record which components are provided by vendors and which have local modifications. A plugin may listen to a Shop-Script event, alter the backend, render storefront elements or process AJAX requests. The official Webasyst plugin development tutorial documents these patterns, including hook handlers and plugin configuration.
Map changes against actual workflows. A revised product hook might touch every category card; a changed order hook could affect downstream stock synchronisation. Ask whether the same data field is written by a warehouse employee, a scheduled import and a marketplace callback. The dependency map needs owners and failure symptoms, not a decorative architecture chart. Keep API tokens out of the document and do not copy customer credentials into test tickets.
Build a recovery point you can actually restore
Before deployment, take consistent backups of the database, application configuration, custom source files, uploaded media and any integration settings needed to rebuild the store. Store an accessible copy away from the production server and check its completion time. The correct recovery scope depends on the update: restoring code alone will not undo a schema migration, while restoring an old database over newly placed orders can lose genuine sales.
Test restoration on a protected environment. Note the time needed, which files and database state are involved, and who has permission to run it. For an active store, recovery must also account for payment notifications and orders created after the backup. A rollback plan can require a carefully sequenced fix-forward or transaction reconciliation rather than blindly replacing the database. State those limits before anyone clicks Update.
Use staging, but keep it from becoming another live shop
A staging copy should reproduce the relevant application versions, theme, plugin set, PHP environment and key settings closely enough to expose incompatibilities. Use synthetic accounts and scrubbed data where practical. Disable outgoing customer email, paid shipping labels, live payment capture and marketplace publication. Restrict staging access and ensure search engines are not encouraged to index duplicate pages.
Test the exact package or changed-file bundle proposed for production. Installing a clean copy of the plugin without the shop's custom theme cannot reveal compatibility issues from overridden templates. Check installation and version metadata, then inspect error logs and background jobs. Keep debugging facilities in staging; production must not expose detailed errors or stack traces to visitors. The value of staging is faithful behaviour, not merely a matching homepage.
Check database changes separately from visual code
Some updates change tables, indexes or configuration in addition to PHP and templates. Webasyst's meta-update documentation explains how update scripts can execute structural changes during installation. Review the proposed database operations, expected run time and whether the change is backward-compatible. Apply them against a copy of representative data before production.
Pay special attention to unique indexes, new required values, timestamps, character encoding and historic rows with missing attributes. A migration that succeeds on ten demonstration products may fail on a large real catalogue. Verify counts, sample records and important relationships after the update. If a migration is not reversible, name that fact explicitly and decide how a failed deployment will be recovered without silently discarding accepted orders.
Test customer journeys and admin workflows
Use a written checklist that covers the first interaction and the final state. On the storefront, open an important category, search by SKU or part number, apply filters, inspect a product, change a variant, add it to the basket, calculate delivery and place a provider-approved test order. Repeat the critical path on a phone and with keyboard navigation. Confirm that prices and availability displayed to customers match the authoritative source.
In the backend, edit a product, receive stock, archive an item, process a sale, inspect order status and confirm the correct notification and log entries. For used items sold across channels, simulate a second listing attempt after stock reaches zero. Test failed API responses and retries as deliberately as the happy path. A check that only records “page loaded” cannot find duplicate order creation, stock drift or a missing marketplace acknowledgement.
Treat payment and shipping integrations as high risk
Payment callbacks and fulfilment actions are not ordinary UI details. A customer may return from the gateway while the server-to-server notification is delayed, duplicated or rejected. Validate the store's final order state and reconciliation identifiers, not just the thank-you page. Check that a repeated callback does not duplicate stock deductions or create a second order. Use a payment provider's sandbox or approved test mechanism whenever available.
For shipping, compare real configuration cases: different postcodes, countries, parcel weights, restricted destinations and free-shipping thresholds. Confirm labels are not accidentally purchased during staging tests. If the update changes authentication scopes or webhook endpoints, coordinate token rotation and callback validation with the relevant provider. Do not publish credentials, order data or personally identifiable information in bug reports.
Include security and permissions in acceptance testing
Check that a staff account can perform only its intended actions, sensitive endpoints reject unauthorised requests and user-supplied content is validated and displayed safely. Review access to logs, upload endpoints, API routes and administrative actions. The OWASP Web Security Testing Guide provides a structured reference for configuration, authentication, authorisation, input validation and business-logic testing. This is guidance for designing tests, not evidence that one quick scan certifies a store as secure.
Keep test results specific: the route tested, role used, expected behaviour, observed behaviour and the corrective action. Treat a plugin update that exposes private order details as a release blocker even if checkout conversion appears unaffected. Security maintenance requires patching and verification; postponing known problems because no customer has complained is not a reliable release strategy.
Deploy with a clear release and rollback decision
Schedule the deployment when a responsible owner can monitor orders and integrations, with an agreed decision point for continuing or reverting. Record versions, changed files, database steps, cache-clearing requirements and the exact time of release. Apply the tested package rather than improvising additional template edits on the live store. Keep a short list of the highest-risk tests for immediate smoke verification.
A realistic go/no-go gate might require successful product search, basket total, shipping choice, test checkout, background queue, stock movement and clean critical error logs. If a check fails, stop further optional changes and assess business impact. Webasyst documents ways to disable ordinary app plugins for troubleshooting, while warning that system shipping, payment and SMS plugins cannot be disabled in the same manner. Never assume every plugin can simply be switched off.
Monitor what happens after release
Observe application errors, payment events, failed jobs, marketplace acknowledgements and customer support messages after the release. Compare a small number of known metrics to the baseline: accepted orders, unusual failures, stock changes and failed API calls. Do not declare success solely because deployment completed. A plugin may fail only when the next scheduled import or payment retry executes.
Log the final versions and defects found, including their resolution. If an unexpected error appears, preserve enough evidence to distinguish the release from a provider outage or an unrelated customer-data issue. Escalate based on customer impact and recover using the previously agreed plan. The record becomes a useful regression checklist for the next upgrade rather than a disposable technical note.
Choose the right level of testing and support
A text-only interface change may need focused checks; a new payment, inventory or checkout plugin deserves a deeper end-to-end test. Prioritise by what the plugin can change, how frequently the feature is used, the reversibility of data changes and whether failure could affect customers or money. The cheapest release is not necessarily the quickest installation; rework, downtime and reconciliation have real costs even when they are hard to price in advance.
For a practical starting point, select one plugin, document its dependencies, prepare a test copy and define five observable acceptance criteria before updating it. Quadro Design works on eCommerce development and connected catalogue workflows. If your Shop-Script store has custom plugins, a sensible project discussion begins with the versions, changed components, integration list and the specific workflows that must remain intact.